The Ultimate 2025 GDPR Compliance Checklist for Websites & SaaS
Comprehensive 2025 GDPR compliance guide covering Articles 6, 13, 17, 28, and 33. Learn exact data subject rights, DPA requirements, cookie consent rules, and statutory proof.
Researched & verified against official statutes (GDPR, CCPA, CUTSA). Reviewed for clarity & accuracy.
What Is GDPR & Who Does It Statutory Apply To?
The General Data Protection Regulation (EU Regulation 2016/679) is the European Union's comprehensive data privacy framework. Enforced since May 25, 2018, it sets strict legal mandates for how personal data is collected, stored, processed, transferred, and deleted.
┌─────────────────────────────────────────────────────────────────────────┐
│              EXTRA-TERRITORIAL SCOPE (GDPR ARTICLE 3)                   │
├─────────────────────────────────────────────────────────────────────────┤
│ Article 3(1): Processing in the context of an EU establishment.         │
│ Article 3(2): Processing of EU residents' data by non-EU entities:      │
│   • Offering goods or services (paid or free) to EU residents.          │
│   • Monitoring behavior of individuals taking place within the EU.      │
└─────────────────────────────────────────────────────────────────────────┘
Statutory Proof (Article 3(2)): If you run a SaaS application, e-commerce store, or mobile app based in the United States, Pakistan, India, or Australia, and you accept signups or track analytics from users located in the EU, GDPR legally applies to you.
The 8 Statutory Rights of Data Subjects (Articles 15–22)
GDPR gives EU individuals ("Data Subjects") enforceable rights over their personal data. As a business ("Data Controller"), you must fulfill these requests within 30 calendar days under Article 12(3):
                     ┌───────────────────────────────────┐
                     │    GDPR DATA SUBJECT RIGHTS       │
                     └─────────────────┬─────────────────┘
                                       │
     ┌──────────────┬──────────────┬───┴──────────┬──────────────┬──────────────┐
     ▼              ▼              ▼              ▼              ▼              ▼
┌──────────┐   ┌──────────┐   ┌──────────┐   ┌──────────┐   ┌──────────┐   ┌──────────┐
│ Article  │   │ Article  │   │ Article  │   │ Article  │   │ Article  │   │ Article  │
│ 15       │   │ 16       │   │ 17       │   │ 18       │   │ 20       │   │ 21       │
│ Right of │   │ Right to │   │ Right to │   │ Restrict │   │ Data     │   │ Right to │
│ Access   │   │ Rectify  │   │ Erasure  │   │ Processing│  │Portability│  │ Object   │
└──────────┘   └──────────┘   └──────────┘   └──────────┘   └──────────┘   └──────────┘
- Right of Access (Article 15): Individuals can request a copy of all personal data held about them free of charge.
- Right to Rectification (Article 16): Individuals can demand correction of inaccurate personal data.
- Right to Erasure / "Right to Be Forgotten" (Article 17): Mandatory deletion of personal data when consent is withdrawn or data is no longer necessary for the original purpose.
- Right to Restriction of Processing (Article 18): Restricting data processing during active accuracy disputes.
- Right to Data Portability (Article 20): Delivering user data in a structured, commonly used, machine-readable format (e.g. JSON or CSV).
- Right to Object (Article 21): Immediate right to opt out of direct marketing and profiling.
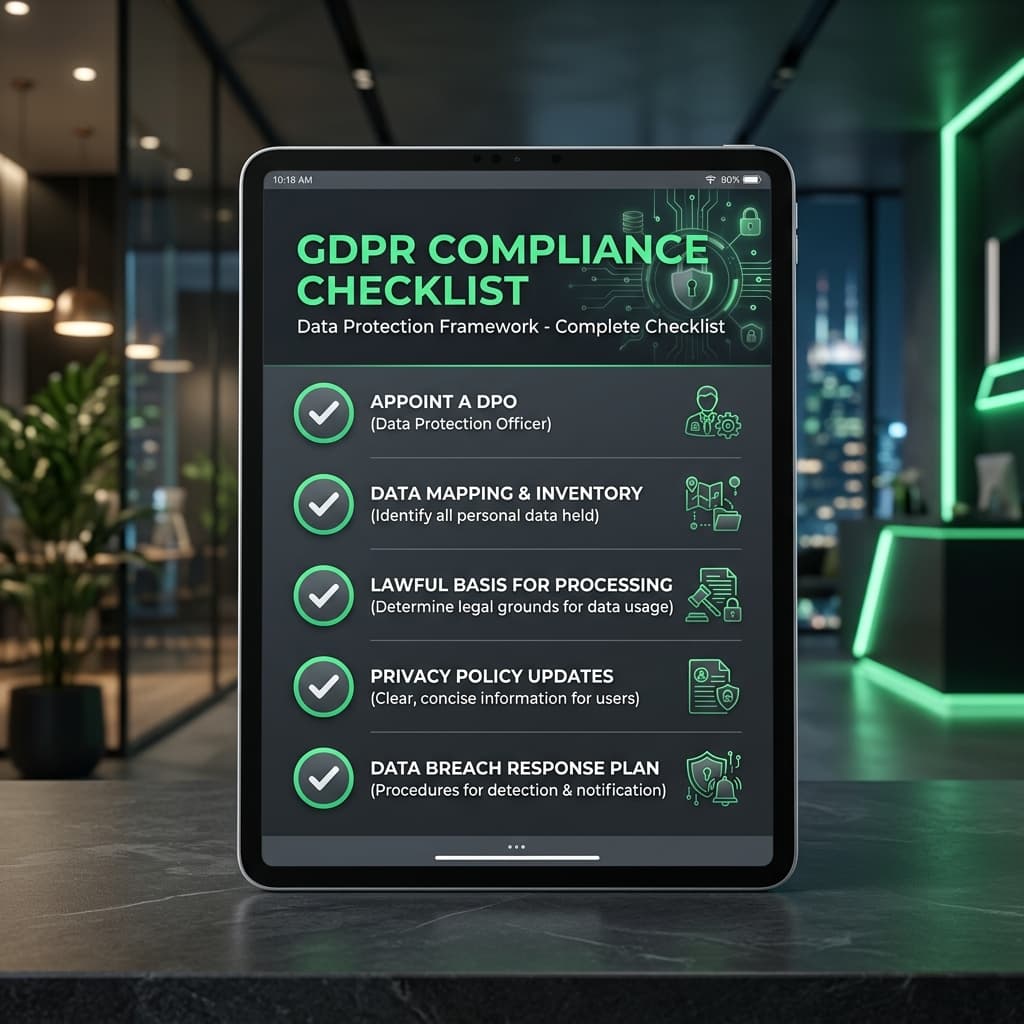
2025 Step-by-Step GDPR Compliance Checklist
1. Identify Your Legal Basis for Processing (Article 6)
Under Article 6(1), processing personal data is unlawful unless at least one of the six legal bases applies:
┌──────────────────────────────────────────────────────────────────────────┐
│                THE 6 LEGAL BASES (GDPR ARTICLE 6(1))                     │
├──────────────────────────────────────────────────────────────────────────┤
│ (a) Consent: Explicit, freely given opt-in.                              │
│ (b) Contract Performance: Necessary to fulfill a contract with user.     │
│ (c) Legal Obligation: Compliance with statutory law (e.g. tax records).  │
│ (d) Vital Interests: Protecting life or emergency health.                │
│ (e) Public Task: Official authority or public interest.                  │
│ (f) Legitimate Interests: Balanced business interest vs privacy impact.  │
└──────────────────────────────────────────────────────────────────────────┘
2. Publish an Article 13 Compliant Privacy Notice
Your privacy policy must contain explicit disclosures required under GDPR Article 13:
- Identity and contact details of the Data Controller.
- Contact details of the Data Protection Officer (DPO), if appointed.
- Specific legal bases used for each processing operation.
- Third-party data recipients (e.g. Stripe, AWS, Google Analytics).
- Data retention periods or criteria used to determine retention.
- Right to lodge a complaint with an EU Supervisory Authority.
Generate a customized notice using ClauseKit's free Privacy Policy Generator.
3. Implement Valid Cookie Consent (ePrivacy Directive & GDPR)
Under CJEU case law (Planet49, C-673/17), cookie consent must satisfy strict standards:
- No Pre-Ticked Checkboxes: Opt-in checkboxes must be un-ticked by default.
- Equal Reject Option: Rejecting non-essential cookies must be as easy as accepting them (1-click Reject All).
- Prior Blocking: Non-essential scripts (Google Analytics, Meta Pixel, Hotjar) must be blocked until positive consent is registered.
4. Execute Data Processing Agreements (Article 28)
When hiring third-party vendors (sub-processors) to handle personal data on your behalf, Article 28 requires a binding Data Processing Agreement (DPA) covering:
- Scope, duration, nature, and purpose of processing.
- Requirement for vendor to process data only on documented controller instructions.
- Guarantee that sub-processor staff are bound by confidentiality.
- Security measures under Article 32 (encryption, pseudonymization).
5. Mandatory 72-Hour Breach Notification (Article 33)
Under Article 33(1), in the event of a personal data breach, the controller must notify the supervisory authority within 72 hours after becoming aware of it. If the breach poses a high risk to individuals' rights, affected individuals must also be notified without undue delay under Article 34.
Comparison: GDPR vs CCPA/CPRA
| Compliance Element | EU GDPR | California CCPA / CPRA | | :--- | :--- | :--- | | Primary Scope | All EU residents' data. | California consumers/households. | | Consent Model | Opt-in (Consent required before collection). | Opt-out ("Do Not Sell or Share My Info"). | | Statutory Fine Max | €20M or 4% of global annual revenue. | $7,500 per intentional violation. | | DPO Requirement | Mandatory for systematic monitoring / large scale data. | Not explicitly required. |
Generate Your GDPR-Compliant Privacy Policy Free
Ensure your website or app meets GDPR Article 13 standards with ClauseKit's free Privacy Policy Generator.
100% Free • No Account Required • Instant PDF & DOCX Download
Frequently Asked Questions
Related Free Legal Tools
Generate custom legal documents relevant to this guide in under 2 minutes. Free PDF & Word download.
Privacy Policy Generator
Create a privacy policy addressing GDPR, CCPA, and CalOPPA requirements for your website or app in minutes.
Terms of Service Generator
Build professional terms of service for your website, app, or SaaS. Protect your IP and limit liability.
Cookie Policy Generator
Create a cookie policy for your website. Covers GDPR, EU Cookie Law, and ePrivacy Directive requirements.
Service Level Agreement (SLA)
Define service quality standards, uptime commitments, support response times, and remedies in a professional SLA.
Free Legal Tools
Ready to protect your business?
Use ClauseKit's free generators to create professional document templates in minutes. No account needed, no credit card required.
Continue Learning
How to Write Terms of Service for a SaaS Product | Full Guide
A practical guide to drafting SaaS terms of service that cover subscription billing, data handling, API usage, uptime commitments, and limitation of liability clauses.
CCPA Compliance Guide for US Businesses | What You Must Do in 2025
A plain-English guide to California Consumer Privacy Act compliance. Covers who it applies to, what rights consumers have, and the privacy policy disclosures you must make.